SPUR is engineered, built, and operated to internationally recognized security, privacy, and operational standards. We separate what we have built to from what we are formally certified for, because customers and regulators deserve that distinction in writing.
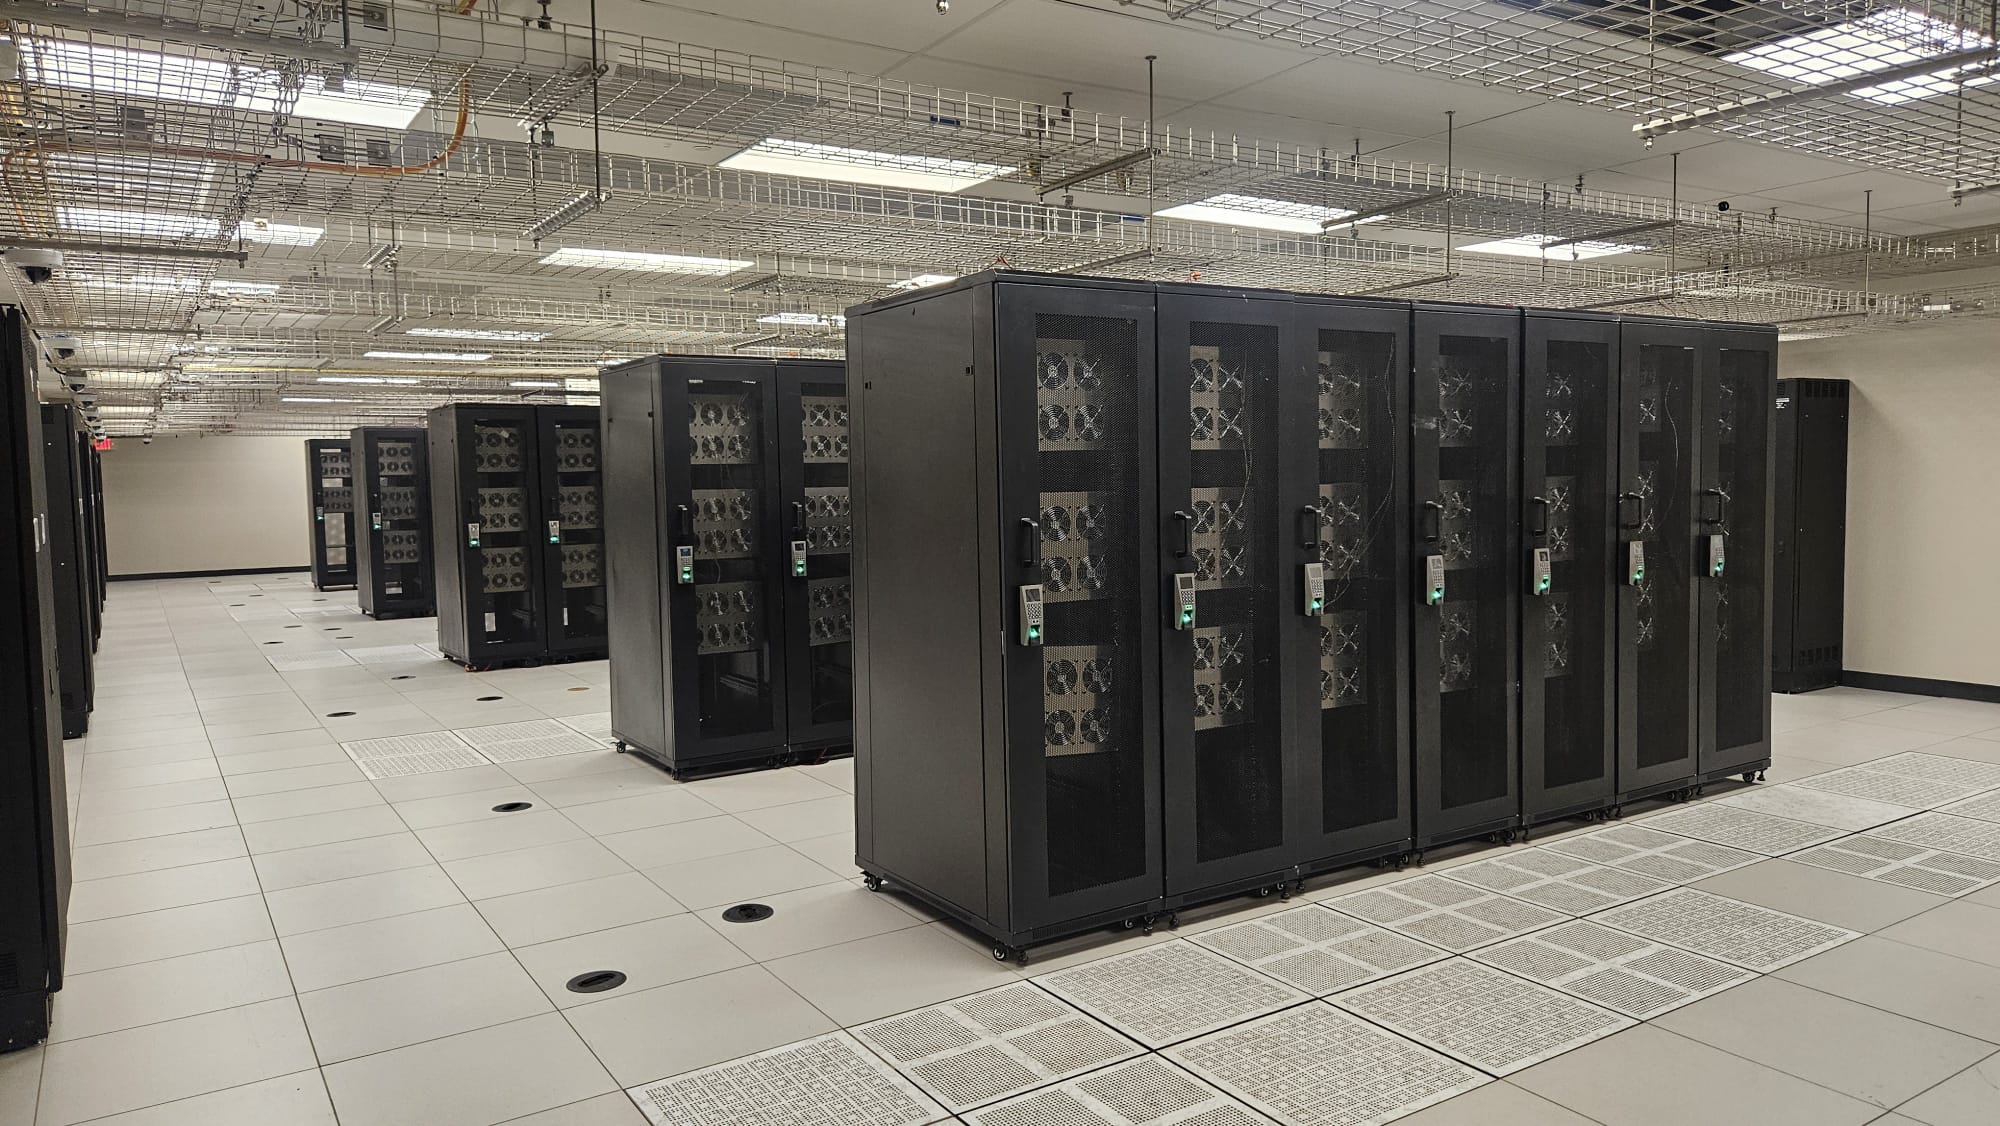
Formal certification is sequenced after the 2026 ISMS rollout. Until then, status is published as engineered-to with control-by-control evidence available under NDA.
| Standard | Scope at SPUR | Status |
|---|---|---|
| SOC 2 Type II | Trust services criteria for security, availability, confidentiality, and privacy across SPUR-hosted services - CSuite, client containers, GPU compute, mail. | Engineered to |
| ISO/IEC 27001:2022 | Information security management system (ISMS) covering data centres, GPU fleet, and the SPUR client-template platform. | Engineered to |
| PCI-DSS v4.0 | Cardholder data handling for any SPUR-operated service that touches payment flows. Stripe is the primary processor; SPUR retains responsibility for segmentation, access, and logging. | Engineered to |
| NIST SP 800-53 / CSF 2.0 | Reference framework for control selection on the data-centre side and for federal and public-sector engagements. | Engineered to |
| CIS Critical Security Controls v8 | Tactical baseline for endpoint, server, and network hardening across the SPUR fleet. Implementation Group 2 (IG2) is the floor. | Adopted internally |
| PIPEDA | Canadian personal data residency by default. All workloads and storage inside Canadian jurisdiction; no cross-border data transfers. | By design |
SPUR Compute and the SPUR Innovation Centre operate end-to-end inside Canadian jurisdiction. No US CLOUD Act exposure. No cross-border data transfers. PIPEDA-compliant by default, with sector-specific controls available for healthcare, financial services, legal, and public-sector tenants. Where the workload requires it, dedicated GPU capacity with no multi-tenancy is available.

SPUR's internal management system (CSuite) maps every operational mutation it logs to a SOC 2 trust-services control through a curated catalogue of audit-event glob patterns. The mapping covers the most material SOC 2 controls. Evidence packets (PDF + CSV) for any date range are generated by an admin in a single click and can be handed to an auditor as-is.
SPUR uses Stripe as the primary processor; SPUR systems do not store, process, or transmit primary account numbers (PAN) directly. Stripe carries PAN responsibility under their PCI Level 1 attestation. SPUR retains responsibility for network segmentation, access controls, logging, and supporting policy - all mapped to PCI controls 1, 2, 4, 7, 8, 10, 11, and 12.
SPUR's information security management system treats Annex A as the control library. The most material controls (A.5.1, A.5.15, A.5.18, A.5.30, A.6.3, A.8.2, A.8.5, A.8.16, A.8.24, A.8.28) are mapped to live audit-event evidence. Full Annex A inventory is maintained in CSuite and available under NDA. Formal certification is on the 2026 ISMS rollout schedule.
Standards on paper are easy. SPUR's operational practice is what produces the evidence. Every host on the fleet is backed up to off-host storage with a tiered local + remote scheme. Restore is tested weekly, not just executed. Monitoring runs every minute across the GPU fleet, data centres, and the application platform. The audit_events table is the immutable system-of-record.
Auditor-ready control mapping and evidence packets are available under NDA. We respond same-day to compliance requests.
